If you store documents, photos, or work files online, the biggest question is simple: “How do I keep them safe?” A strong security and privacy setup is more than a checkbox—it’s a set of decisions you make around encryption, access controls, and sharing. This guide focuses on one practical need: how to reduce exposure when you use dropbox.com for file storage and collaboration.
Instead of trying to cover every privacy feature, we’ll zoom in on what matters most for everyday safety. You’ll learn how encryption protects data, how permissions and links affect who can view or edit files, and which sharing behaviors help you avoid common mistakes. If you want a supporting reference that complements a broader “security overview,” this article is built for that intent.
Encryption Basics You Can Verify in Your Daily Workflow
Encryption is the foundation of many modern privacy protections because it helps ensure that data is unreadable to unauthorized parties. In practical terms, encryption turns readable content into ciphertext so that even if something intercepts data in transit, the content remains difficult to interpret without the right keys. For services like dropbox.com, encryption is typically applied across important data paths, including when files are uploaded and when they are downloaded.
However, encryption isn’t useful only as a concept—it should fit into how you use the service. Start by assuming that encryption protects your files while they move between your device and the provider, but your access controls still matter once files are stored and shared. In other words, strong encryption reduces the risk of interception, while access controls reduce the risk of unauthorized access.
To make encryption part of your routine, focus on two habits. First, keep your app and browser updated so you avoid known security gaps that can undermine secure connections. Second, treat shared links and invited collaborators as part of the security model—encryption won’t stop someone who is already allowed to access the file.
Encryption in Transit vs. Encryption at Rest
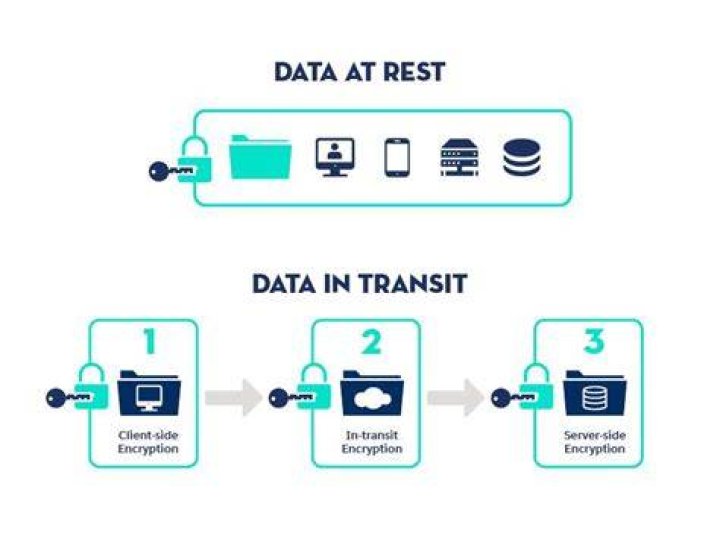
When people say “encryption,” they often mean different things. Encryption in transit protects data while it’s moving, such as during upload or download. Encryption at rest protects data while it’s stored, helping prevent unauthorized parties from reading stored content if they were to access raw storage.
These two layers work together. Even if a connection is protected during transfer, the stored file should still be protected if the storage layer is compromised. Likewise, if stored content is protected, encryption in transit still helps defend against interception on the network path.
Access Controls: The Real Difference Between Safe Sharing and Risk
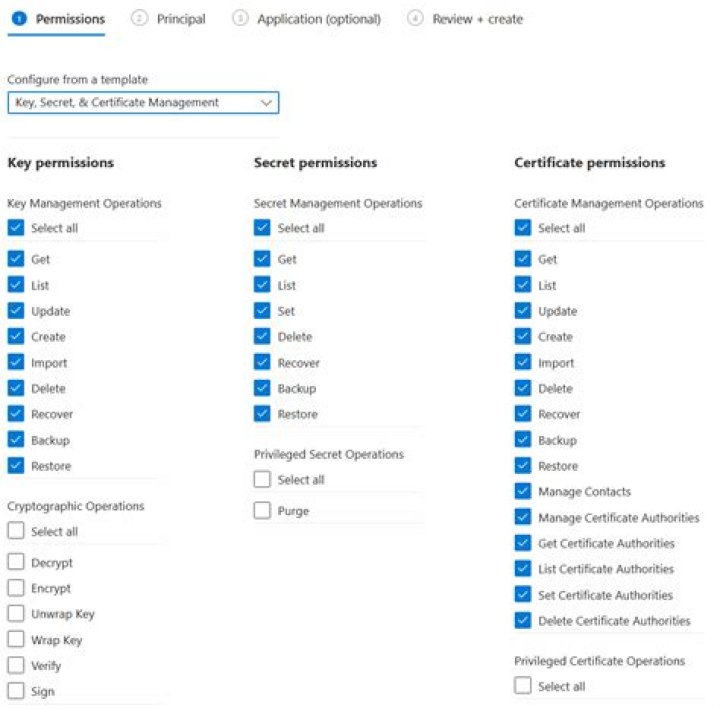
Encryption is valuable, but access control is what determines who can actually view, download, or edit your files. This is where many real-world incidents begin: a file is encrypted, but it’s shared too broadly or with the wrong permissions. When you use dropbox.com, your goal should be to minimize the number of people who can access sensitive content and to ensure each person gets the correct level of access.
Think of access control as three layers: identity, permission scope, and sharing method. Identity answers “who are you?” Permission scope answers “what can you do?” Sharing method answers “how did you receive access?” Together, they reduce the likelihood of accidental exposure.
Invites, Membership, and Least-Privilege Permissions
Whenever possible, prefer access methods that tie permission to an identity. If a collaborator is invited by account, you can better manage who has access and remove access later if circumstances change. That’s more reliable than a link that anyone with the URL can use.
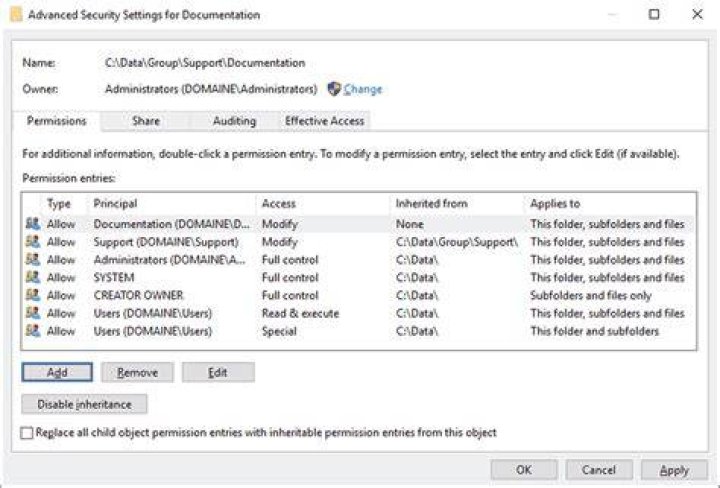
Next, align permissions with the task. Many teams default to broad access when a narrower role would work. The “least privilege” approach asks a straightforward question: does this person need to view only, or do they truly need to edit?
When you apply least privilege, you reduce the impact of both mistakes and account compromise. If a user only has view access, they can’t easily alter the file or introduce changes. If their access is removed, the file is effectively locked down again.
- Prefer identity-based access: invite collaborators rather than relying solely on public links.
- Use minimal permissions: grant edit access only when required.
- Review access regularly: remove access after projects end or roles change.
Link Sharing: Convenience with Security Tradeoffs
Link sharing is often useful for quick collaboration, but it can be risky if you don’t manage it carefully. Links can be forwarded, saved, or shared unintentionally. Even if the file remains encrypted, link exposure can still lead to unauthorized viewing.
To reduce this risk, treat links as “capabilities” that can travel beyond your intended audience. If you must use a link, choose the safest option available for your workflow, and consider adding additional constraints such as limiting access to specific people or requiring authentication.
Also, take inventory of links over time. If a link was created for a one-time review, don’t leave it active indefinitely. Instead, revoke or rotate links when the review is complete.
Multi-Factor Authentication and Account Safety That Complements Encryption
Encryption protects your data in storage and transit, but account access protects your ability to control sharing. If someone gains access to your account, they may be able to view files you’ve shared, modify permissions, or create new links. That’s why strong authentication matters.
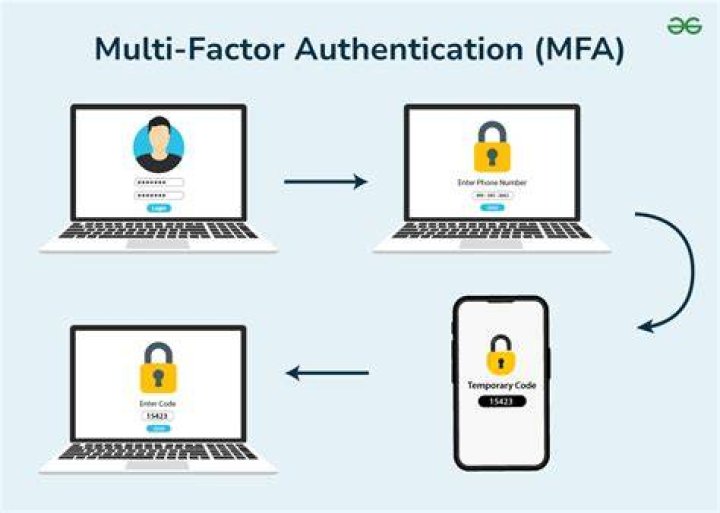
Multi-factor authentication (MFA) adds a second verification step beyond your password. In many threat scenarios, passwords alone are the weakest link because they can be guessed, reused, or exposed through phishing. MFA helps prevent unauthorized login even when credentials are compromised.
For maximum safety, enable MFA for your dropbox.com account and also protect any linked email accounts. Email is often the gateway for password resets, so securing it helps prevent attackers from taking over your identity and then your files.
Why Phishing Still Matters to File Security
Phishing attacks don’t need to break encryption. They aim to steal credentials so the attacker becomes “authorized.” Once authorized, the attacker’s actions can be as dangerous as a direct breach of storage.
Watch for login prompts, attachment traps, and fake sign-in pages. A safer habit is to navigate to the service yourself (for example, by using bookmarks) instead of clicking “sign in” links from unexpected emails. If something looks unusual, treat it as a red flag.
Sharing Safety: Practical Habits That Reduce Exposure
Security features help, but your behavior determines how often those features are used correctly. The safest sharing routine is consistent, deliberate, and easy to audit later. When you share through dropbox.com, focus on preventing oversharing and maintaining clear control over what each person receives.
Start with content classification. Ask whether the file is sensitive—financial records, HR documents, internal strategies, or personal information. Sensitive content should use tighter sharing options, shorter lifespans for links when possible, and identity-based access.
Audit Shared Items and Keep Collaboration Boundaries Clear
A common problem is “set it and forget it.” Links remain active, permissions remain broad, and former collaborators keep access longer than needed. A simple audit routine prevents this drift.
Once per month (or per project milestone), check what you shared, with whom, and whether edit access is still necessary. If access is no longer needed, revoke it promptly. If a collaborator only needed temporary review, rotate the link or replace it with a more restricted method.
Also, avoid sharing entire folders when a single file would work. Folder sharing can unintentionally expose additional documents that weren’t meant to be included. If you can share a specific file or a curated folder, you reduce accidental exposure.
Use Version Awareness to Prevent Unwanted Changes
When multiple people collaborate, versions can become confusing. If someone edits the wrong file or overwrites a critical version, you may lose integrity even without data theft. Access controls reduce unauthorized changes, but process matters too.
Create a clear workflow: define who can edit, who reviews, and what version becomes final. If your team uses comments or review workflows, keep the editing scope narrow so the final version remains controlled. This improves both safety and accuracy.
Device and Network Hygiene: The “Last Mile” of Privacy
Even with strong encryption and access controls, your device and network can introduce risk. If your endpoint is compromised—through malware, browser hijacking, or insecure downloads—attackers may capture data before it reaches encrypted storage. That’s why endpoint safety is part of a complete security approach.
Keep operating systems and browsers updated, use reputable antivirus or endpoint protection, and avoid downloading suspicious files that could carry malware. If a device is shared among multiple people, ensure accounts are separated and each user logs out when finished.
Network hygiene matters too. Public Wi-Fi can be riskier if you use insecure settings. If you need extra protection on untrusted networks, consider using a trusted connection method such as a VPN, and always avoid entering sensitive credentials on sketchy captive portals.
Session Management and Logout Discipline
Session safety is overlooked because it feels basic. Yet leaving sessions active on shared computers or unattended devices can expose your account to unauthorized use. If you sign in on a shared machine, log out when done.
Also, be cautious about staying signed in on public or unmanaged devices. A strong account setup helps, but physical access to an open session can bypass many online protections.
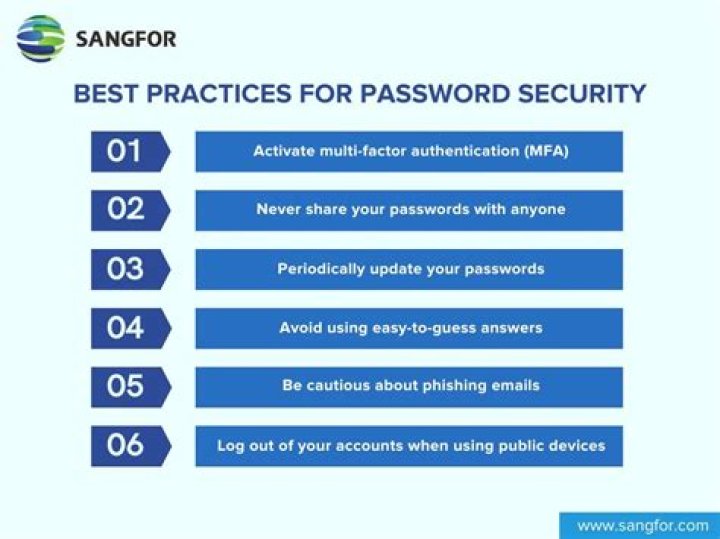
Putting It Together: A Simple Security Checklist for dropbox.com File Safety
If you want a practical way to apply everything above, use a checklist that you can actually follow. The best security setup is the one you maintain. With dropbox.com, you can build safety through encryption-aware sharing, access control discipline, and authentication protection.
Here’s a focused checklist you can reuse for individuals and teams.
- Enable MFA: protect your account against credential theft.
- Use identity-based sharing: invite people when possible instead of relying only on public links.
- Apply least privilege: grant view vs edit based on real needs.
- Review links and permissions: revoke access when reviews finish or roles change.
- Audit folder scope: share specific files or curated folders for sensitive work.
- Practice endpoint hygiene: keep devices updated and be cautious on public networks.
- Log out on shared devices: avoid leaving active sessions unattended.
When you follow these steps, you’re not just relying on “the service is secure.” You’re actively shaping risk. That’s what turns encryption and access controls into real privacy results.
Final Thoughts
Online security works best when you combine platform protections with smart sharing habits. By understanding encryption basics, controlling access with least privilege, and strengthening account safety with MFA, you can significantly reduce the risk of unauthorized exposure. When you use dropbox.com with these practices, you’re not only storing files—you’re managing them with confidence.
Sources
Keep Learning
