When you rely on a service like megakino for day-to-day tasks, security and privacy stop being “technical details” and start being part of your real-life risk management. The goal of this guide is simple: help you use megakino safely by understanding the most common threats, what they look like, and what you can do to reduce exposure.
Instead of trying to cover everything in one place, this article focuses on one high-intent topic—safe use of megakino while minimizing privacy leaks and account compromise. If you’ve ever wondered why a login fails, why an alert feels suspicious, or how “permissions” can affect what gets collected, you’re in the right spot.
Start With Threat Modeling for Your megakino Use
Before changing settings, it helps to identify what you’re trying to protect. Most privacy and security incidents around online services fall into a few predictable buckets: account takeover, phishing and social engineering, data over-sharing, and exposure through insecure devices or networks.
Think of your risk as a combination of who might target you and what would be valuable if they did. For example, if you reuse passwords, an attacker only needs one breach to attempt credential stuffing. If you allow excessive permissions, an app or browser session may access more than you intended.
Here’s a practical way to model threats for your megakino activity: list your most important actions (logins, payments, messaging, file uploads, integrations), then note the most likely attackers (scammers, malicious websites, compromised devices) and the most likely impact (unauthorized access, tracking, leaked personal data). When you understand the “why,” best practices become easier to apply.
Secure Your Account First: Password, MFA, and Session Hygiene
Your account is the primary gateway for both security and privacy. If an attacker gets in, they can often view data, reset settings, and use your access to contact others or change integrations. That’s why the safest megakino setup begins with account hardening.
Use a unique password that you do not reuse across other services. Password reuse is one of the most common drivers of account takeover because it turns one breach elsewhere into an “instant win” for attackers. A strong password manager can help you create and store high-entropy credentials without making you memorize anything.
Enable multi-factor authentication (MFA) wherever it’s available. MFA adds a second barrier so that stolen passwords alone are not enough. If you get a choice, prioritize MFA methods designed to resist phishing and relay attacks.
Review active sessions and sign out of devices you no longer use. Long-lived sessions can persist after lost phones, shared laptops, or “forgotten” browser tabs. Session hygiene is especially important if you access megakino from public Wi‑Fi, a work device with multiple users, or a family computer.
Know the Signs of Account Takeover Attempts
Look for behavioral cues rather than guessing. If you receive login alerts you didn’t trigger, notice unexpected changes in profile details, or see new devices listed under your account, treat it as a potential compromise. Attackers often probe quietly first, then escalate once they confirm access.
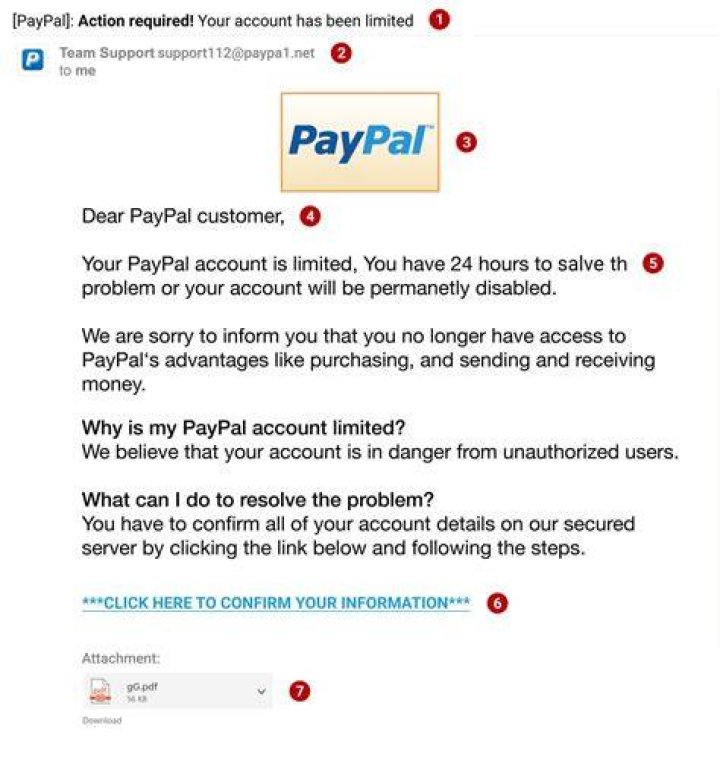
Also be cautious with “support” messages delivered through email or in-app chat. Phishers frequently impersonate legitimate services and ask you to verify details urgently. When in doubt, navigate to megakino directly by typing the address yourself or using a trusted bookmark instead of following a link from the message.
Reduce Phishing and Social Engineering Risk in Real Time
Phishing is not just fake emails anymore—it includes fake login pages, malicious attachments, and convincing “verification” prompts. The most effective defense is to develop a habit of slowing down when you see an urgent request.
Use these checks before entering any credentials related to megakino or your account in general:
- Check the sender and domain carefully. Subtle differences in spelling or lookalike domains are a common giveaway.
- Do not trust urgency. Messages that claim “your account will be locked” or “confirm within 10 minutes” are designed to bypass careful review.
- Inspect links without clicking blindly. If a link doesn’t match the expected domain for megakino, treat it as suspicious.
- Verify requests for sensitive actions. If someone asks for your password, one-time codes, or recovery details, assume it’s a scam.
In practice, you want a “verification loop”: if the message feels urgent, you open a new tab, navigate to the service yourself, and confirm whether any security action is genuinely needed.
Be Careful With Recovery and “Verification” Codes
Recovery flows can be exploited. If you receive a code you didn’t request, you may need to lock down your account quickly by changing your password and reviewing sessions. In many attack chains, the attacker triggers a password reset to gain control while you’re distracted.
Never share one-time codes with anyone, even if they claim to be support. Legitimate systems do not require you to disclose MFA codes to “help” you log in.
Control Privacy Exposure: Permissions, Data Sharing, and Tracking
Security and privacy overlap, but they are not identical. Even if your account is safe, you can still create privacy exposure by granting unnecessary permissions or allowing data sharing you didn’t intend to authorize.
Start by reviewing what permissions you grant in browsers, mobile apps, and any connected services. Overbroad permissions can increase the chance that information is accessible to features you rarely use. For example, allowing broad access to contacts or files may not be necessary for typical megakino tasks.
Next, check privacy-relevant settings tied to:
- Profile visibility (what others can see)
- Communication settings (who can contact you, and what is discoverable)
- Integration controls (which third parties can access data)
- Tracking preferences (if you have options related to analytics or personalization)
When you change settings, do it intentionally. The best privacy improvement often comes from removing permissions you don’t need and tightening visibility rules rather than chasing every tracking detail.
Understand What “Connected” Services Can Mean
Many privacy incidents begin with integrations. If you connect megakino to other tools (calendars, storage, messaging, productivity suites), those connections can increase the surface area for data access. It’s not automatically unsafe to integrate, but you should treat connections like doors: fewer doors, better locks.
Periodically audit connected accounts and remove any integration you no longer use. If an integration was created by a previous workplace or a past personal workflow, it may be outdated and still requesting access.
Use Safe Browsing Practices on Devices and Networks
Even strong account protections can be weakened by insecure device and network habits. If malware is present or if you’re on an untrusted network, attackers can intercept sessions, capture credentials, or track activity.
For safe megakino use, focus on three layers: the device, the browser, and the network. Keep your operating system and browser up to date, because security fixes are often time-sensitive. Avoid downloading unknown software that claims it will “boost performance” or “secure your privacy,” since many are actually tracking or malware wrappers.
On the network side, be careful with public Wi‑Fi. Public networks are not inherently dangerous, but they are where attackers can try man-in-the-middle tactics and session hijacking. If you must use public Wi‑Fi, consider a reputable VPN and avoid logging into sensitive accounts on shared machines.

Browser Hygiene That Prevents Privacy Leaks
Privacy can leak through browser behaviors: saved autofill data, cached pages, and persistent cookies. When using megakino on shared or temporary devices, sign out and consider using a private browsing mode if appropriate for your situation.
Also be aware of how browser extensions work. Extensions can read and modify web content. If an extension is not necessary, disable or remove it to reduce the risk of tracking scripts or malicious behavior.
Recognize and Respond to Security Incidents Fast
Security is not only about prevention. It’s also about speed of response. When something goes wrong—unexpected logins, suspicious emails, unusual account behavior—the fastest path to recovery usually includes containment and verification.
If you suspect compromise related to your megakino account, follow a simple incident checklist:
- Change your password immediately (use a unique one).
- Enable or verify MFA if it was disabled or you suspect settings were altered.
- Sign out of all sessions and revoke access from unknown devices.
- Review recent security actions and check for modified profile or connected services.
- Scan your device if you downloaded suspicious files or noticed unusual activity.
Then, watch for “second-wave” attacks. Attackers may attempt new logins after the first one fails. A proactive review of session history and integrations can stop these loops.
Keep Evidence Without Spreading It
If you receive suspicious messages, avoid forwarding them broadly. Instead, preserve key details such as timestamps, sender information, and the subject line. This helps you compare what happened against the security timeline inside your megakino account.
If you later report the incident, clear context speeds up resolution. In most cases, what matters is not emotional urgency but accurate sequencing.
Best Practices Checklist You Can Use Every Week
Most privacy and security improvements come from small routines repeated consistently. If you want a weekly habit, use this short checklist tied to megakino safe use.
- Review active sessions and sign out of devices you don’t recognize.
- Check connected services and remove anything you no longer use.
- Confirm privacy settings (visibility, sharing controls, and permission scopes).
- Look for unusual alerts such as login notifications or password reset events.
- Update your device and browser to the latest stable versions.
This routine is designed to be practical rather than perfect. If you only do one thing, start with account protections and permissions; they deliver the biggest risk reduction for most users.
How megakino Can Fit Into a Safer Setup (Without Overcomplicating)
Using megakino safely doesn’t require you to become a security engineer. The strongest approach is to combine account hardening, careful browsing habits, and periodic permission audits into a predictable workflow.
For many people, the most noticeable improvements come from enabling MFA, removing unnecessary permissions, and tightening how devices handle sessions. When those controls align, megakino becomes less of a “data risk” and more of a tool you can trust.
Final Thoughts
A secure, privacy-respecting experience is built from everyday choices: unique passwords, MFA, session hygiene, careful permission management, and quick response to suspicious activity. If you apply these practices consistently, you’ll reduce the most common risks that threaten accounts and personal data while using megakino with confidence.
Sources [U.S. Cybersecurity and Infrastructure Security Agency (CISA)](https://www.cisa.gov/) — guidance on phishing, account security, and incident response. [National Institute of Standards and Technology (NIST) Special Publications](https://www.nist.gov/publications) — digital identity and authentication guidance. [FTC Consumer Advice](https://consumer.ftc.gov/) — practical tips on scams and account safety.
