When you use a service for communication, collaboration, or everyday online tasks, “security & privacy” stops being a buzzword and becomes a practical requirement. People want to know what’s collected, how it’s protected, who can access it, and what happens if something goes wrong.
This supporting guide focuses on one specific question behind many searches: what to know about security and privacy when you’re choosing and using winnoise. You will not find vague promises here. Instead, you’ll get a clear checklist of concepts, the questions to ask, and the settings that typically matter most.
Start with the basics: what “security” vs “privacy” really mean
Security is about protecting data and systems from unauthorized access, tampering, or misuse. Privacy is about limiting how personal information is collected, used, shared, and retained. Even though these terms overlap, they lead to different checks.
For example, strong security can still allow privacy risk if data is collected for broader purposes than you intended. Likewise, privacy controls may not help if attackers can bypass protections. Understanding the difference helps you evaluate both.
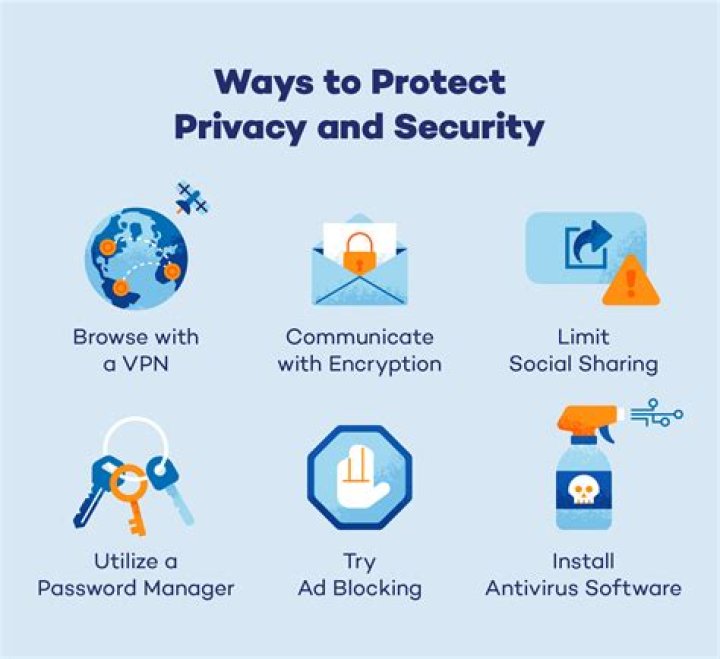
In the context of winnoise, treat security as “how it protects your data” and privacy as “how it handles your information.” That framing makes it easier to spot red flags and also to identify the features that genuinely reduce risk.
Encryption: the cornerstone of protecting data in transit and at rest
Encryption is one of the most important mechanisms for protecting confidentiality. “In transit” encryption protects data as it moves between your device and the service. “At rest” encryption protects stored data against threats like disk theft or unauthorized database reads.
When evaluating security & privacy, look for encryption that covers both scenarios. Many services use TLS (Transport Layer Security) for connections, and additional encryption for stored records. However, the details matter: encryption strength, key management practices, and whether backups are protected.
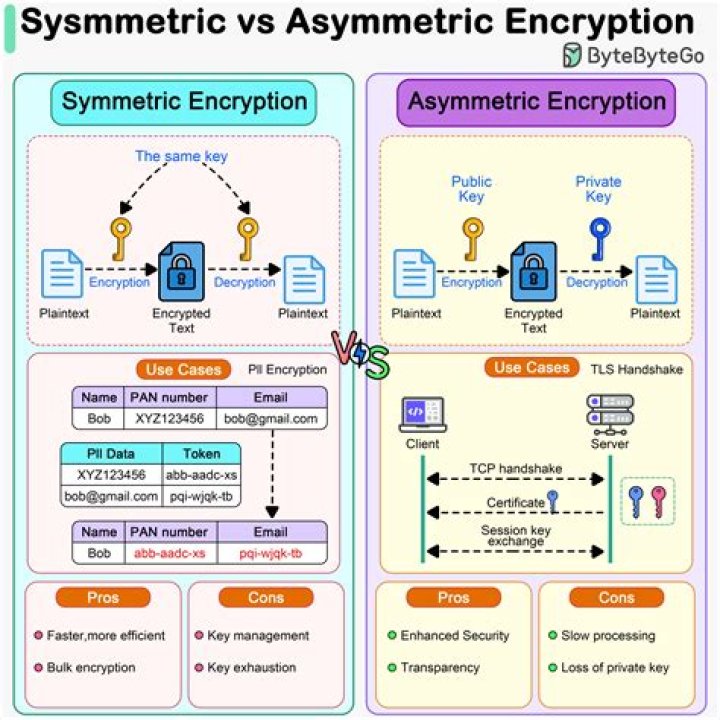
Practical takeaway: if a platform supports secure connections (often indicated by HTTPS and modern TLS), that is a baseline. If it also provides strong encryption for stored content, it improves your protection if a data breach occurs.
Account protection: access controls that reduce the impact of compromise
Even with encryption, accounts can be compromised through weak passwords, phishing, reused credentials, or lost devices. That is why access controls are central to real-world security. The best platforms reduce risk with controls that make unauthorized access harder and easier to detect.
For winnoise, the key areas to look for typically include secure sign-in methods, role-based access, session protections, and the ability to revoke access when needed. The goal is to limit “blast radius” if a login is compromised.
Use strong authentication and reduce credential reuse
Multi-factor authentication (MFA) adds a second layer beyond the password. While MFA is not a magic shield, it significantly improves protection against password guessing and many phishing attempts. Password managers also help by generating unique credentials.
If a service supports MFA, you should use it. If it doesn’t, that is a factor to consider when comparing options for security and privacy.
Session management: what happens when you log out or change devices
Session controls determine how long a signed-in state stays valid and how it can be ended. A strong setup allows you to view active sessions and revoke them. That becomes crucial after you lose a phone or suspect someone else accessed your account.
In addition, device and session hygiene matters: regularly signing out on shared devices and enabling prompts for unusual activity can reduce exposure.
Data minimization and retention: fewer records can mean less risk
Privacy risk often grows with the amount and lifetime of stored data. Data minimization means collecting only what is necessary for the service to function. Data retention policies define how long the service keeps records after they are no longer needed.
From a security & privacy standpoint, minimization reduces the value of stolen data and limits the impact of an incident. Retention controls can also reduce long-term exposure if you forget about a piece of information.
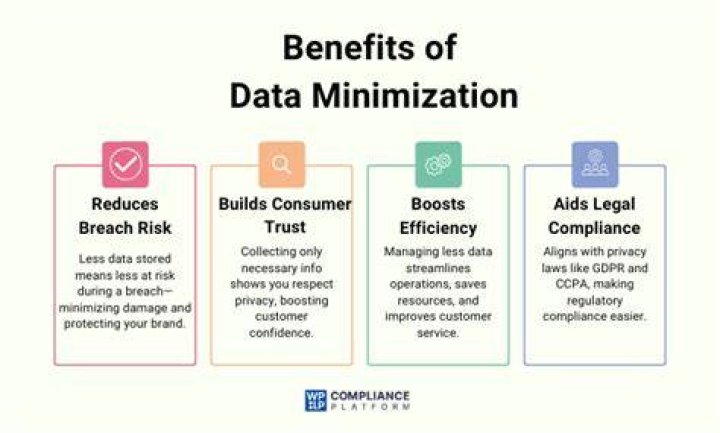
When you evaluate winnoise, look for clarity on what is stored (for example, account details, activity logs, or messages) and how long it is retained. If the service is transparent about retention windows and deletion options, you have more ability to protect your privacy proactively.
Privacy controls: transparency, settings, and user data rights
Privacy is not only about what a company can do; it is also about what you can control. Effective privacy controls help you understand what is collected and allow you to manage it.
Many privacy frameworks emphasize transparency and user choice. In practice, that can include clear settings for visibility, permissions, marketing communications, and data-sharing features.
Check the defaults before you share anything
Defaults often determine your initial privacy posture. If visibility is too broad or permissions are overly permissive, you may share more than you realize. A good approach is to review settings soon after creating an account.
For winnoise users, treat the first configuration as a security action: review privacy toggles, permissions, and any optional features that affect data exposure.
Know how requests and deletions work
Privacy policies typically describe how to request access to your data, correct errors, or request deletion. The timeline and scope matter—some services delete data from primary storage quickly but keep backups for a period.
If you care about privacy, you should understand the mechanics: what is deleted, what is archived, and what is retained for safety, legal, or fraud prevention reasons.
